Benefits of Private Hosting Solutions in Enterprise Scaling
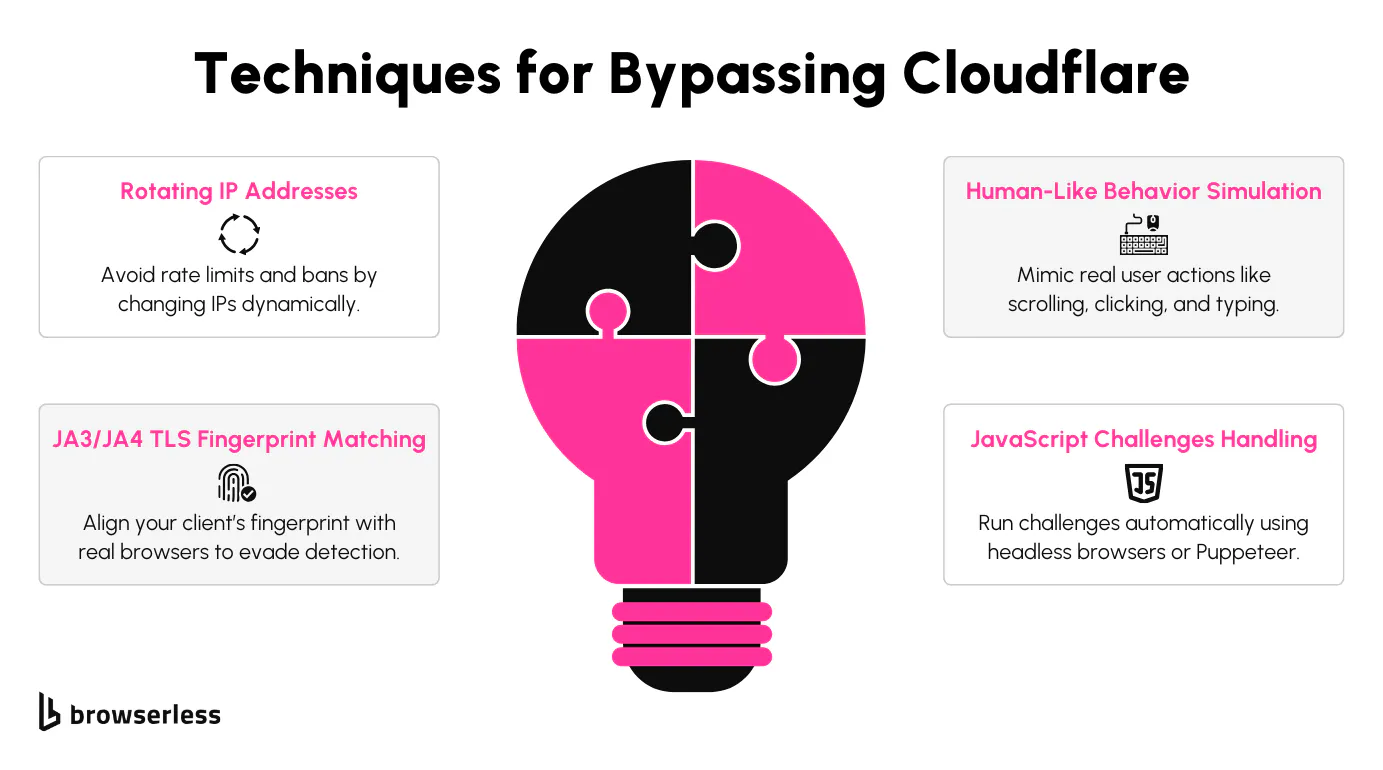
A lot of scrapers get blocked at layers 3-4, not 5-7. repairing one layer while neglecting others will not work these catch 55% of bots before JS even runs but they're triggered by invisible signals mouse motion and timing matter more each year usage bot detection websites to audit your setup even ideal stealth can't avoid all challenges For managing the CAPTCHA layer when it triggers, examine out passxapi-python it supplies a unified API for reCAPTCHA, hCaptcha, Turnstile, and FunCaptcha, so you can focus on the other layers.
In this tutorial, you will discover the following: What Cloudflare is. A much deeper take a look at its WAF system. How its anti-bot system works from a technical perspective. What takes place when you target a Cloudflare-protected website utilizing standard automation tools. Top-level approaches to bypass Cloudflare. How to bypass the Cloudflare human check in Python.
It provides a detailed suite of services developed to make sites quicker and more secure., caching website material on a global network to enhance load times and reduce latency.
Strategies for Scale Global Infrastructure with Automation
By integrating with Cloudflare's network, sites can quickly get enhanced security and optimized performance. This can be enabled on any web page served through its international network.
More specifically, the Cloudflare WAF sits in front of your web applications. It checks and filters incoming demands in real time to stop attacks or undesirable traffic before they reach your servers or access your websites. As part of its multilayered defense technique, the Cloudflare WAF utilizes proprietary algorithms to find and obstruct malicious bots.
It looks at information like the cipher suites used, the order of settlement, and other low-level traits. Bots typically recycle default or suspicious configurations that vary from those utilized by real browsers.
This consists of the exact internet browser variation, running system, installed fonts or extensions, and even subtle hardware attributes. These information points form a fingerprint that helps differentiate real users from automated scripts.: Among the greatest indicators of automated traffic is abnormal habits. Cloudflare displays patterns like rapid demands, lack of mouse movements, identical click courses, idle times, and more.
XrumerHigh-Speed API Solutions and OCR Solving
Cloudflare typically offers 2 modes of human confirmation: Constantly reveal the human confirmation difficulty Automated human verification challenge (only when suspicious activity is identified) Explore both choices below! The idea is to constantly need human confirmation on the first access to a website.
Try visiting it in incognito mode (to make sure a fresh session without any cookies), and you will see a CAPTCHA called Cloudflare Gate, even if you are a real human user:: By the time you read this post, StackOverflow's bot security might have altered or be working differently. In this case, if you are building an automated script, the only alternative is to automate the Gate CAPTCHA interaction in a human-like way.
That is how it handles to verify you are human with a single click. In this mode, Cloudflare just provides a challenge if it thinks a demand might be from a bot. It does this by presenting a JavaScript challenge, which runs invisibly in the web browser to confirm that the client acts like a legitimate user: This procedure is smooth and normally finishes immediately if you are a human using a routine web browser.
Because this triggers minimal interruption for routine users, it is by far the most typical Cloudflare mode. If the JavaScript challenge stops working (significance Cloudflare concludes the client is likely to be a bot), it will escalate to showing a Turnstile CAPTCHA for human confirmation: Now, you are back to what you saw in the previous circumstance.
This page is secured by the Cloudflare WAF, so the automated JavaScript-based verification process will right away begin. In the background, a series of POST requests are exchanged with Cloudflare's endpoints, sending encrypted data within their payloads: The precise contents of these payloads are not openly recorded.