Choosing Dedicated Server Solutions in 2026
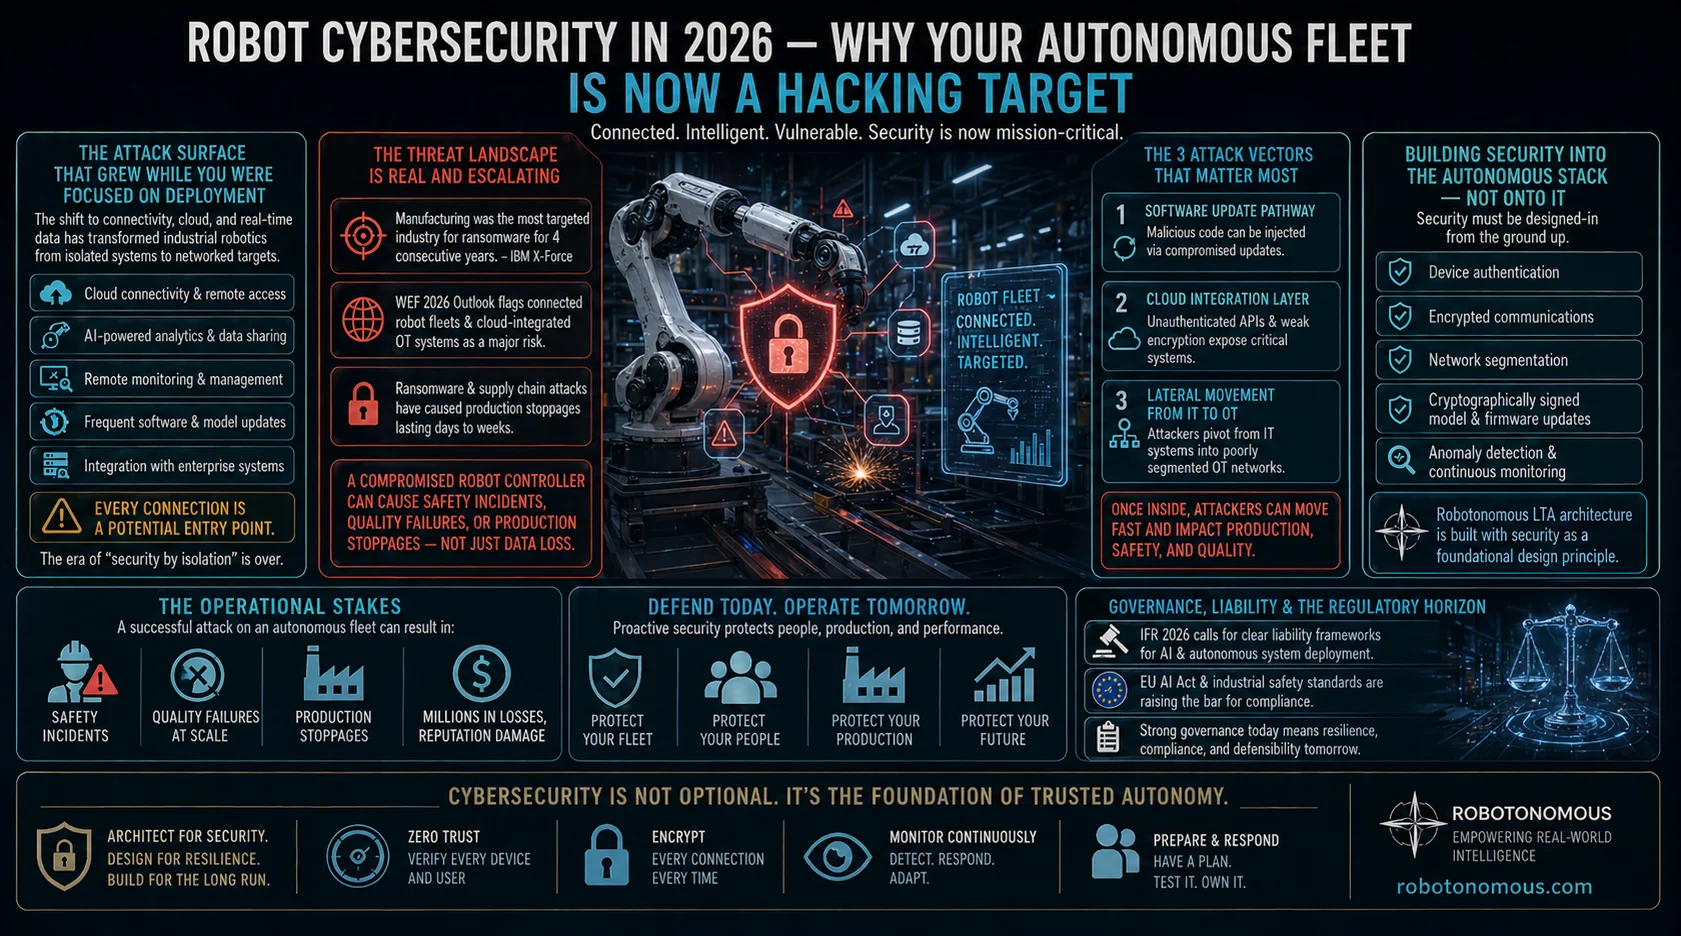
Danger actors have increasingly shifted focus from conventional codeinjection attacks to more comprehensive supply chain compromise methods. CSO Online exposes that 3 in 5 companies (71 %) experienced a material thirdparty security event in 2025.
This more comprehensive danger landscape needs holistic supply chain security methods. Organizations should deal with software application and hardware, facilities services, and constant thirdparty danger monitoring. As organizations rely more on cloud, containers, and APIs, assaulters exploit weak points throughout all 3 to bypass conventional security layers. According to SQ Magazine's cybersecurity attacks data 2026 report, containers and cloud misconfigurations are contributing to risk.
This is why security needs to deal with the full stack. It should comprise cloud platforms, container orchestration, and API endpoints rather than treating them as separate domains. Integrated controls and runtime observability have become necessary defenses. Functional Innovation (OT), Industrial IoT (IIoT), and other important facilities systems are no longer peripheral targets.
This increased direct exposure broadens the attack surface, driven by gaps in setup management and delayed patching practices. From energy grids to manufacturing lines, interruptions in OT/IoTcontrolled environments can lead to safety risks, service interruptions, and financial loss.
How Bot Detection Is Evolving in 2026
Attackers are shifting their focus to the human layer using more sophisticated and deceptive methods., deepfake AI-led fraud cases surged by 1,300% year-over-year.
Hence, companies should validate sensitive demands utilizing numerous channels and train workers to acknowledge deepfake efforts. They ought to execute AI-based detection tools to flag suspicious audio or video communications. It's essential to enforce stringent approval workflows for financial or gain access to requests and screen for anomalous behaviour patterns even when interactions appear genuine.
Cybersecurity has become a business necessity, not simply an IT concern. As business speed up digital transformation, adopt AI technologies, scale their cloud systems, and assistance hybrid work, cyber risks are developing faster than ever. Opponents are getting quicker, smarter, and advanced. They utilize expert system, automation, and social engineering to discover and make use of weak points faster than previously.
XEvil 6 Beta standalone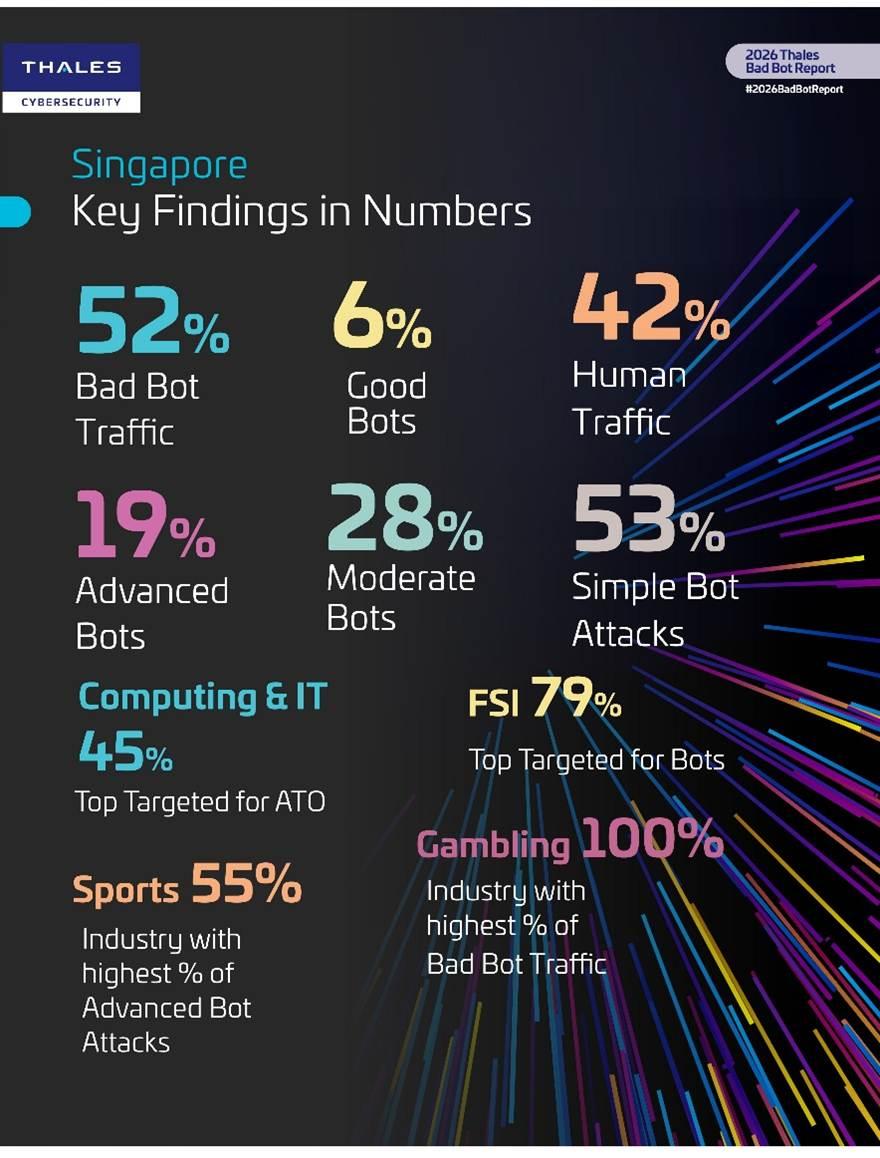
In 2026, businesses require to move from responding to threats to constructing proactive cyber durability. Now, cybercriminals use AI to automate phishing, produce persuading deepfakes, bypass conventional security steps, and find vulnerabilities much faster than previously.
Produce reasonable voice and video deepfakes. Automate vulnerability discovery Evade traditional detection systems. Introduce intelligent malware that adapts during execution. Organizations ought to utilize AI-powered security tools that spot unusual behavior, not just rely on signature-based detection. AI-driven threat detection Behavioral analytics Device discovering for anomaly detection Security automation Traditional security that concentrates on the network boundary is ending up being outdated.
Best Practices for Distributed Networks in the AI Era
It's no longer safe to trust users simply because they're on the business network. follows one basic principle: "Never Trust. Always Verify." Organizations are implementing: No Trust assists lower the threat of attacks and provides much better exposure to users and devices. It produces a more regulated and clearer security environment.
Rather of assaulting firewall programs, enemies progressively target user identities through credential theft, session hijacking, OAuth abuse, and MFA tiredness attacks. Modern identity protection now includes: Password less authentication Identity Risk Detection & Reaction (ITDR) Adaptive authentication Privileged Gain access to Management (PAM) Continuous identity tracking Organizations that concentrate on identity-first security lower the threat of account breaches.
That's why security teams are building stronger cloud defenses. Security groups are investing in: Cloud Security Posture Management (CSPM) Cloud Work Protection Platforms (CWPP) Cloud-Native Application Defense Platforms (CNAPP) API security Container security Kubernetes security Security is now being developed right into cloud deployment pipelines.
As a result, organizations are making supply chain security a leading concern. Organizations now prioritize: Software application Expense of Products (SBOM) Safe SDLC Code signing Dependency scanning Continuous vulnerability monitoring Third-party threat evaluations Supply chain security is no longer optional.