Comparing High-Performance Virtual Server Options
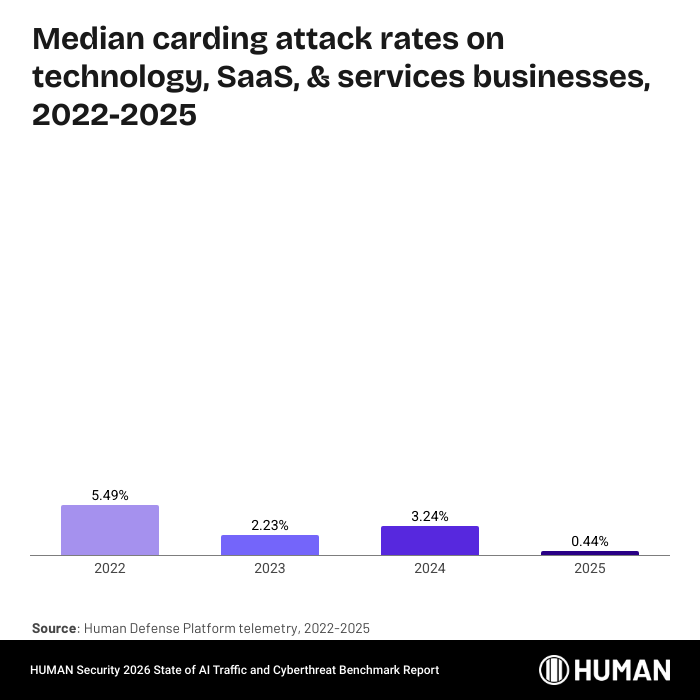
from our Security Operations and Intelligence division. Cyber hazard actors (CTAs) are progressively creating payloads that can perform across Windows, Linux, and even macOS, minimizing the need for separate codebases and increasing their reach. We'll likely see more unified structures capable of jeopardizing blended environments with a single campaign. The malware itself will likely be more of the very same we'll still be talking about infostealers, loaders, ransomware, and spyware and much of it will come from familiar families.
premium XEvil proxiesWe're seeing glimpses of automation already, such as credential theft, worm-like propagation, and automated payload delivery. While effective and effective, neither of these threats nor any other present malware are fully autonomous.
That evolution could considerably shorten the time in between preliminary gain access to and full compromise. CTAs will try out generative AI (GenAI) and code-assist tools to accelerate malware development, improve obfuscation, or develop polymorphic variants on need. We'll likely see minimal case-by-case examples of this rather than prevalent adoption in 2026, as advances in development will still fall brief of constant operational use.
Why Bot Detection Must Adapt in 2026
GenAI has also become the terrific equalizer for numerous cybercriminals. What pre-owned to take specialty abilities and hours of extreme effort can now be dealt with in a matter of minutes leveraging tools anyone can gain access to. From automating analysis of stolen information to profiling targets to developing incorrect identities to leveraging GenAI's capacity for natural language, cybercrime has ended up being more accessible to a wider audience of prospective risk actors than ever in the past, and we're likely to see increased usage of GenAI for Crimeware as a Service.
Instead of counting on quickly flagged IPs or domains that create traffic jams for detection, enemies are turning to credible platforms such as content shipment networks and SaaS suppliers to host credential gathering pages and other malicious content. Fake login pages hosted on legitimate domains may be removed rapidly, so enemies are looking for opportunities to merely spin up brand-new subdomains at speed and scale to keep persistence.
We have actually seen a clear shift in how enemies consider impact. They're no longer material with hitting one company at a time. Instead, they're targeting the connective tissue of our digital environment: software application suppliers, handled service providers, and other single points of failure. These kinds of security events underscore how a single compromise can cascade throughout sectors and have global effect for hours or perhaps days.
Community networks are tempting targets due to the fact that they are deemed less defended, loaded with rich data, and important to the material of our society. 2026 could see a hazardous convergence of increasing attack focus and decreasing protective capacity, with the MS-ISAC being among the few organizations positioned to help minimize the risk at scale.
Analyzing Cybersecurity Trends in 2026
While the current open LLMs are not proper RAGs, there is most likely to be a shift in 2026 towards RAG models. These designs integrate skilled information with external sources to produce more prompt and appropriate actions than a model might create on its own. From a risk point of view, this might introduce new threats in the form of model poisoning, sensitive data leakage, and direct exposure of exclusive information if not executed thoroughly and if those external understanding sources are not thoroughly controlled.
2026 is an election year, implying that. Operational Innovation (OT) and critical facilities will experience a high-impact cyber event, most likely connected to a geopolitical dispute, which will lastly activate. after another major SaaS outage interferes with emergency or public services, speeding up multi-cloud and "cloud failover" architectures. even as they are progressively hired to shoulder greater responsibility in protecting their jurisdictions and vital facilities against a growing wave of advanced cyber dangers.
Local networks are tempting targets because they are considered as less defended, full of abundant information, and critical to the material of our society. 2026 might see an unsafe convergence of rising attack focus and diminishing protective capacity, with the MS-ISAC being among the couple of companies positioned to help reduce the threat at scale.
While the current open LLMs are not proper RAGs, there is most likely to be a shift in 2026 toward RAG models. These designs integrate skilled data with external sources to produce more prompt and pertinent actions than a model could generate by itself. From a danger perspective, this could introduce new dangers in the kind of design poisoning, delicate information leak, and exposure of exclusive data if not executed thoroughly and if those external understanding sources are not thoroughly managed.
2026 is an election year, meaning that. Functional Technology (OT) and crucial facilities will experience a high-impact cyber occurrence, likely connected to a geopolitical conflict, which will finally set off. after another major SaaS blackout disrupts emergency situation or civil services, accelerating multi-cloud and "cloud failover" architectures. even as they are increasingly called upon to carry higher obligation in defending their jurisdictions and critical infrastructure versus a growing wave of sophisticated cyber threats.