Future Cybersecurity Trends: Access Management

They monitor and assess inbound and outgoing traffic based upon predefined security guidelines, allowing legitimate communication while obstructing suspicious or unapproved gain access to efforts. Modern firewall programs go beyond standard filtering by offering deep packet evaluation, application awareness, and intrusion avoidance capabilities, making them a vital element of network protection. Anti-virus and anti-malware services protect networks and linked systems from harmful software application such as viruses, worms, trojans, ransomware, and spyware.
Virtual private networks (VPNs) supply safe and secure and encrypted interaction channels over public or untrusted networks. They are commonly utilized to safeguard remote gain access to connections, making sure that delicate information transmitted between users and network resources remains private.
NAC systems evaluate user qualifications, gadget identity, and security posture before approving access, ensuring that only compliant and authorized devices connect to the network. This helps in reducing dangers from unmanaged devices, jeopardized systems, and insider hazards. An invasion detection and prevention system (IDPS) constantly keeps track of network traffic to identify suspicious patterns, abnormal behavior, and known attack signatures.
By combining detection and avoidance abilities, IDPS boosts presence into network activity and supports proactive danger management. With essential services covered, let's concentrate on the advantages of network security. Network security uses several advantages, consisting of:: Assists prevent unapproved gain access to, malware, and other attacks that can jeopardize systems and data.
Network Security Fundamentals for Automation Developers
: Lowers downtime by preventing attacks that can interfere with network services and operations.: Helps companies meet legal, industry, and regulative security requirements. Finally, let's go through a few of the very best practices for carrying out network security successfully. Apply these finest practices to make sure robust and reliable network security:: Enforce intricate passwords, multi-factor authentication (MFA), and regular credential updates.
: Protect information in transit and at rest utilizing strong encryption protocols.: Find unusual habits early through continuous tracking and log analysis. In this guide, we had a detailed discussion on network security basics, covering what it is, its core principles, and how it works. We analyzed typical network security hazards and crucial solutions for alleviating them.
The 3 pillars of network security are:: Safeguards sensitive information by limiting gain access to solely to authorized users and avoiding any unapproved disclosure.: Maintains the accuracy and integrity of data by preventing unauthorized adjustment or alteration.: Guarantees that systems, networks, and information remain available to licensed users when needed.
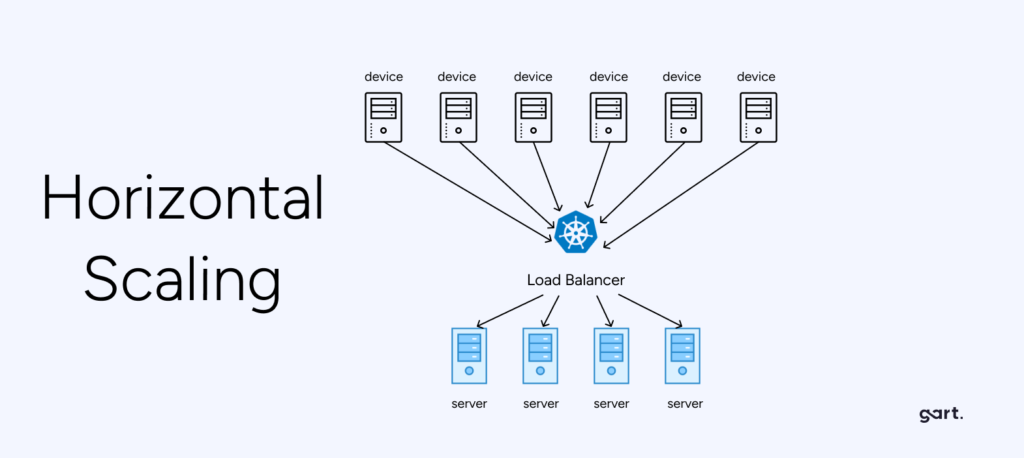
Scaling Cloud Hardware for Heavy Automation
Network security essentials describes the policies, tools, and practices that keep computer networks and the data moving through them safe from unauthorized gain access to, misuse, or interruption. It is not one single item however a layered approach combining innovation, procedure, and individuals. For novices, understanding the core pillars, typical risks, and everyday controls turns a challenging subject into something workable and actionable.
Stability safeguarding information from being changed or damaged by unauthorized parties. Accessibility keeping systems and information available to legitimate users when required. These three goals, frequently called the CIA triad, guide choices about which manages to release and how to focus on restricted resources. Networks deal with a large range of risk vectors, much of which exploit human habits or weak configurations: Malware malicious software such as infections, worms, ransomware, and spyware that infiltrates endpoints or servers.
Man-in-the-middle (MitM) attacks interception of interactions in between 2 parties, typically on unsecured networks. Denial-of-service (DoS) and distributed DoS (DDoS) flooding a system with traffic to make it unavailable. Unpatched vulnerabilities known software defects that aggressors make use of before updates are applied. Carrying out network security essentials implies releasing a set of overlapping controls that collaborate to decrease threat.
XEvil 6 Beta standaloneNext-generation firewalls go further by including deep packet assessment and application awareness. Encryption scrambles data so only authorized parties can read it. Protocols like TLS safeguard data in transit, while disk and database file encryption protect data at rest. Strong access control limits what users and gadgets can do when they are inside the network.
The three pillars of network security are:: Secures sensitive information by restricting gain access to solely to licensed users and avoiding any unapproved disclosure.: Keeps the accuracy and integrity of data by preventing unauthorized modification or alteration.: Ensures that systems, networks, and information stay available to licensed users when required.
XEvil 6 Beta setupOptimizing Cloud Infrastructure for Heavy Workloads
Network security basics describes the policies, tools, and practices that keep computer networks and the data moving through them safe from unauthorized access, abuse, or disruption. It is not one single product but a layered technique integrating technology, process, and individuals. For novices, understanding the core pillars, typical hazards, and daily controls turns a challenging subject into something workable and actionable.
Integrity securing information from being modified or corrupted by unauthorized celebrations. Schedule keeping systems and data available to legitimate users when required. These 3 goals, typically called the CIA triad, guide choices about which controls to deploy and how to prioritize minimal resources. Networks face a large range of risk vectors, much of which make use of human habits or weak setups: Malware destructive software such as viruses, worms, ransomware, and spyware that infiltrates endpoints or servers.
Man-in-the-middle (MitM) attacks interception of communications between two celebrations, frequently on unsecured networks. Denial-of-service (DoS) and distributed DoS (DDoS) flooding a system with traffic to make it unavailable. Unpatched vulnerabilities known software application flaws that aggressors exploit before updates are used. Implementing network security essentials implies releasing a set of overlapping controls that work together to minimize threat.
Encryption scrambles data so only authorized celebrations can read it. Procedures like TLS safeguard data in transit, while disk and database file encryption protect information at rest.