High-Speed VPS Rental for SEO
Network supervisors can put devices on different network sectors, while they may likewise be geographically far-off. They are all. Networks come in a variety of types. Security measures required vary depending on network configurations. Typical versions consist of: Regional Area Networks or are small community devices linked through several routing nodes.

LAN networks can consist of numerous different devices. A LAN could feature computers, smart devices, printers, IoT gadgets, tvs, and video gaming consoles. Routers assign IP addresses to all devices, which determine them on the network. Wide Area Networks are more typical in modern-day company. They constitute collections of LANs and cover broad geographical areas.
The web itself is defined as a WAN. Every ISP is also technically a WAN. Software-defined Wide location networks are laid over WAN networks. Agents on connected devices link users to network resources. Supervisors can control gain access to via protected entrances, and SD-WAN enables in-depth traffic tracking. Companies likewise tend to utilize SD-WAN to secure cloud possessions successfully.
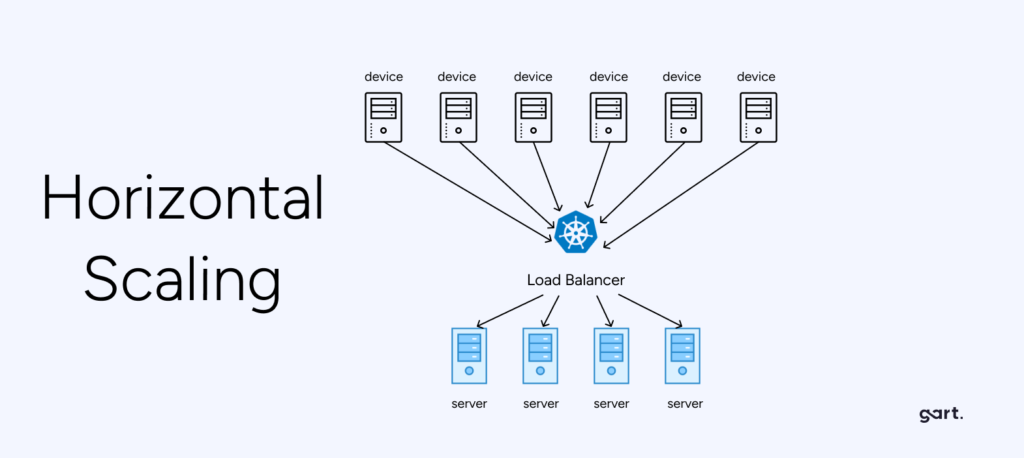
The network layer is where data is transferred. Servers produce packages of details, which they send out to network devices via routing devices.
Comparing Free OCR Services Online
File encryption hides the contents of packages, securing them against external observers. Network devices are any items of hardware linked to the network architecture. Every network should be recorded and mapped. Mapping allows supervisors to understand which devices need protection. Business networks normally rely on a number of gadget types: store info and software application.
- interact information across the network. supplement the router and divert traffic effectively. connect network areas together. - connect to router gadgets and allow staff protected access. connect areas of the network with different procedures or security profiles. - guards network edges versus destructive traffic. offer wireless gain access to for authorized devices.
XEvil 6 Beta standaloneIt also inspects the status of network devices such as servers or switches and informs network supervisors when faults occur. Tracking can be Proactive monitoring is more suitable, expecting problems and seeking dangers before they cause damage. Tracking can likewise be agent-based or agentless: This type of tracking. Representatives connect to central monitoring software.
Future Cybersecurity Strategies: Access Automation
This information might consist of memory usage and procedures running on the device. Agents may track user connections or examine basic performance. Agent-based monitoring delivers granular details and improves network exposure. The proliferation of representatives postures issues. Security groups should reserve time to upgrade and log representatives. Managing big communities of agents can be difficult for smaller companies.
It involves package inspection to discover information about data and network use. And it can likewise involve app monitoring to make sure just confirmed users have gain access to. Agentless monitoring is non-intrusive and requires few resources. It provides a data stream that can be used to improve security setups. This details is normally not granular.
Monitoring is not always consistent. Rather, security supervisors to assess functionality and security status. The space in between security evaluations is the tracking interval. Periods vary depending upon gadget type and situation. Technicians arrange continuous examinations of the internal network. Nevertheless, basic network efficiency measurements may have longer keeping track of intervals. This reduces the load put on the network.
Securing networks also extends to access control, network organization, and security policies. Networking security is. Both feed into protecting a single computer system linked to the network infrastructure against outside risks.
Identity Security Systems in 2026
A well-thought-out security method balances gain access to and defense while likewise meeting compliance objectives. There are numerous networking security policy active ingredients.
Gain access to management entrances make sure only users with the proper credentials can access network properties. Security policies define access levels.
Firewall securities also avoid illicit gain access to. app security makes sure the appropriate configuration of applications working on the network. The code of apps can be vulnerable to external attacks. For example, assaulters exploit vulnerabilities in app code to gain access to network resources. Application security tests all apps and applies spots to update code.