How to Circumvent Modern Automation Systems
Network supervisors can place gadgets on various network segments, while they might likewise be geographically remote. However they are all. Networks been available in a range of types. Security steps required differ depending on network configurations. Common variations consist of: Regional Area Networks or are small neighborhood devices linked through one or more routing nodes.

LAN networks can consist of several devices. A LAN might include computer systems, smart devices, printers, IoT devices, tvs, and video gaming consoles. Routers assign IP addresses to all gadgets, which recognize them on the network. Wide Location Networks are more typical in contemporary service. They constitute collections of LANs and cover wide geographical areas.
The web itself is defined as a WAN. Every ISP is likewise technically a WAN. Software-defined Wide area networks are laid over WAN networks. Representatives on linked gadgets connect users to network resources. Managers can manage access by means of secure gateways, and SD-WAN enables extensive traffic tracking. Business likewise tend to utilize SD-WAN to protect cloud assets effectively.
The network layer is where data is transmitted. Servers create packages of info, which they send to network devices through routing devices.
Why Residential Proxies Improve Bot Success
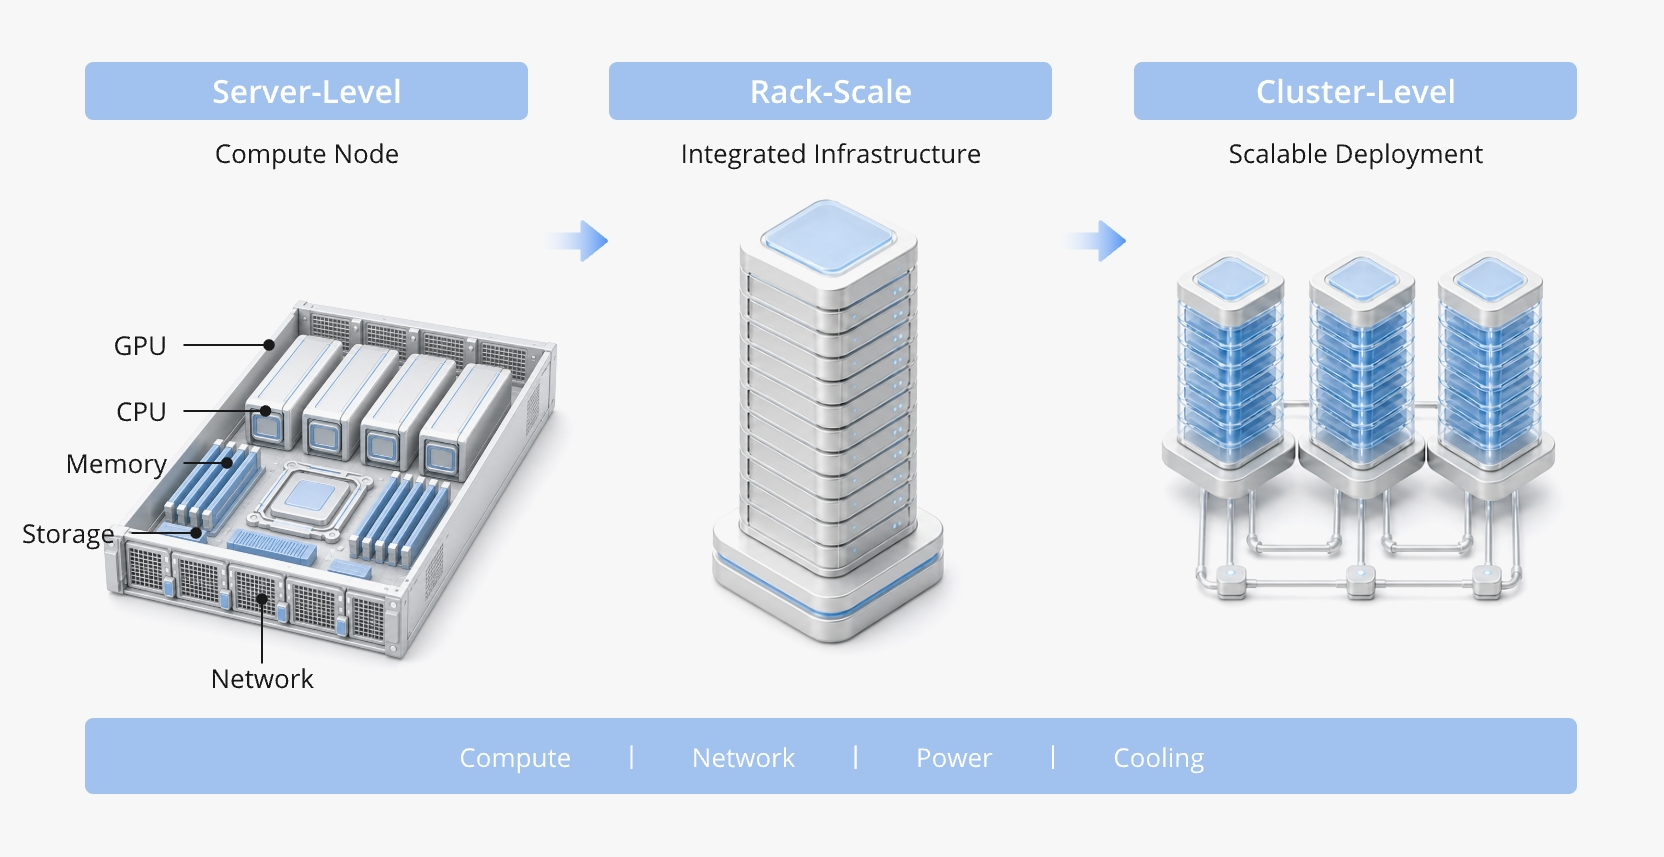
File encryption conceals the contents of packages, securing them against external observers. Network gadgets are any products of hardware linked to the network architecture. Every network needs to be documented and mapped. Mapping makes it possible for supervisors to comprehend which devices require security. Business networks typically depend on a number of device types: store info and software application.
- interact info across the network. - link to router gadgets and allow personnel protected gain access to. - guards network edges versus malicious traffic.
It also inspects the status of network gadgets such as servers or switches and informs network managers when faults take place. Tracking can be Proactive tracking is more effective, preparing for problems and seeking hazards before they cause damage. Monitoring can likewise be agent-based or agentless: This kind of monitoring. Representatives connect to central monitoring software application.
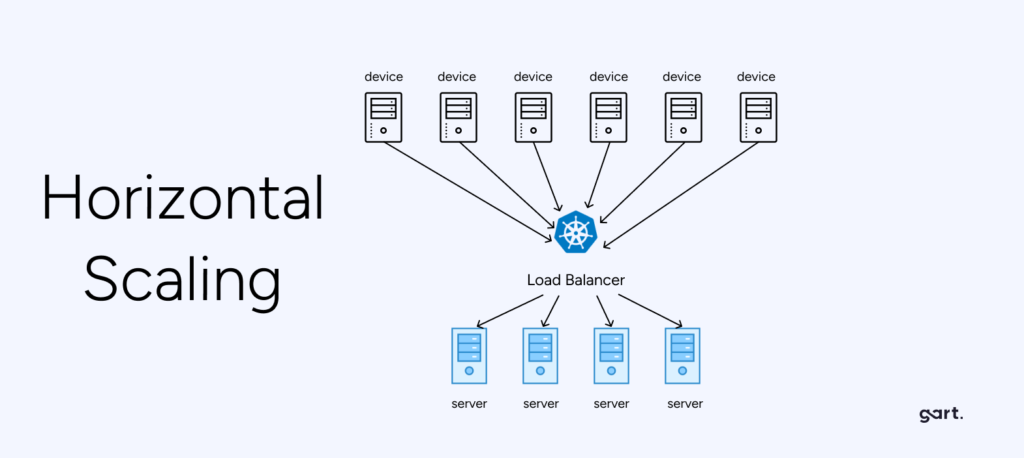
Scaling Cloud Hardware for Heavy Automation
This data could include memory use and procedures working on the gadget. Agents may track user connections or evaluate general performance. Agent-based monitoring delivers granular information and enhances network exposure. However, the proliferation of agents positions issues. Security teams should reserve time to update and log representatives. Managing big neighborhoods of representatives can be hard for smaller companies.
It includes packet assessment to find info about data and network usage. And it can also include app monitoring to ensure only authenticated users have gain access to. Agentless monitoring is non-intrusive and needs few resources. It provides an information stream that can be used to improve security setups. But this details is usually not granular.
Technicians set up constant assessments of the internal network. Basic network performance measurements might have longer keeping track of periods. This reduces the load positioned on the network.
Protecting networks likewise extends to access control, network organization, and security policies. Networking security is. Both feed into safeguarding a single computer system connected to the network facilities against outdoors threats.
XEvilHow to Bypass Advanced Bot Detection
Services depend upon dependable access to work and databases. However, they need to secure private information from external observers via information security methods. A well-thought-out security technique balances access and protection while also fulfilling compliance goals. There are numerous networking security policy ingredients. Common approaches include: firewall softwares are the foundation of most security setups.
Access management gateways guarantee just users with the appropriate credentials can access network possessions. Security policies specify access levels.
Firewall securities also avoid illegal gain access to. app security makes sure the correct setup of applications working on the network. The code of apps can be susceptible to external attacks. Assailants make use of vulnerabilities in app code to gain access to network resources. Application security tests all apps and uses spots to update code.