Identity Management Systems in 2026
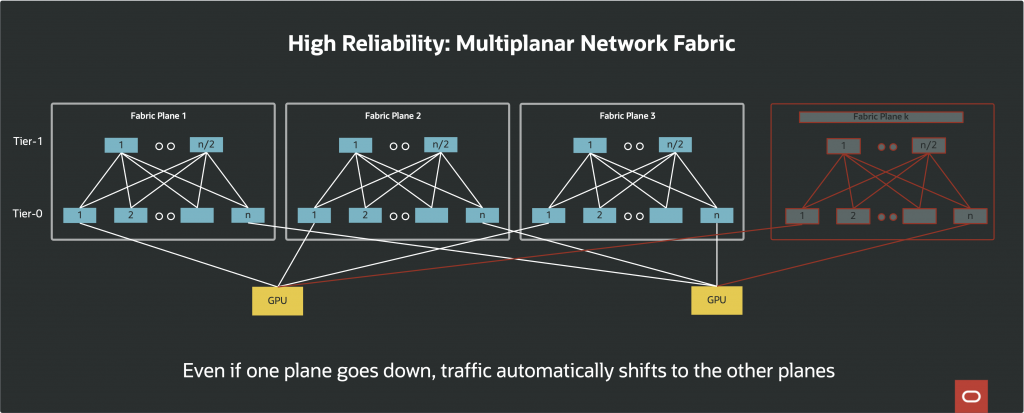
Network managers can put devices on various network segments, while they may also be geographically far-off. Security measures required vary depending on network setups.
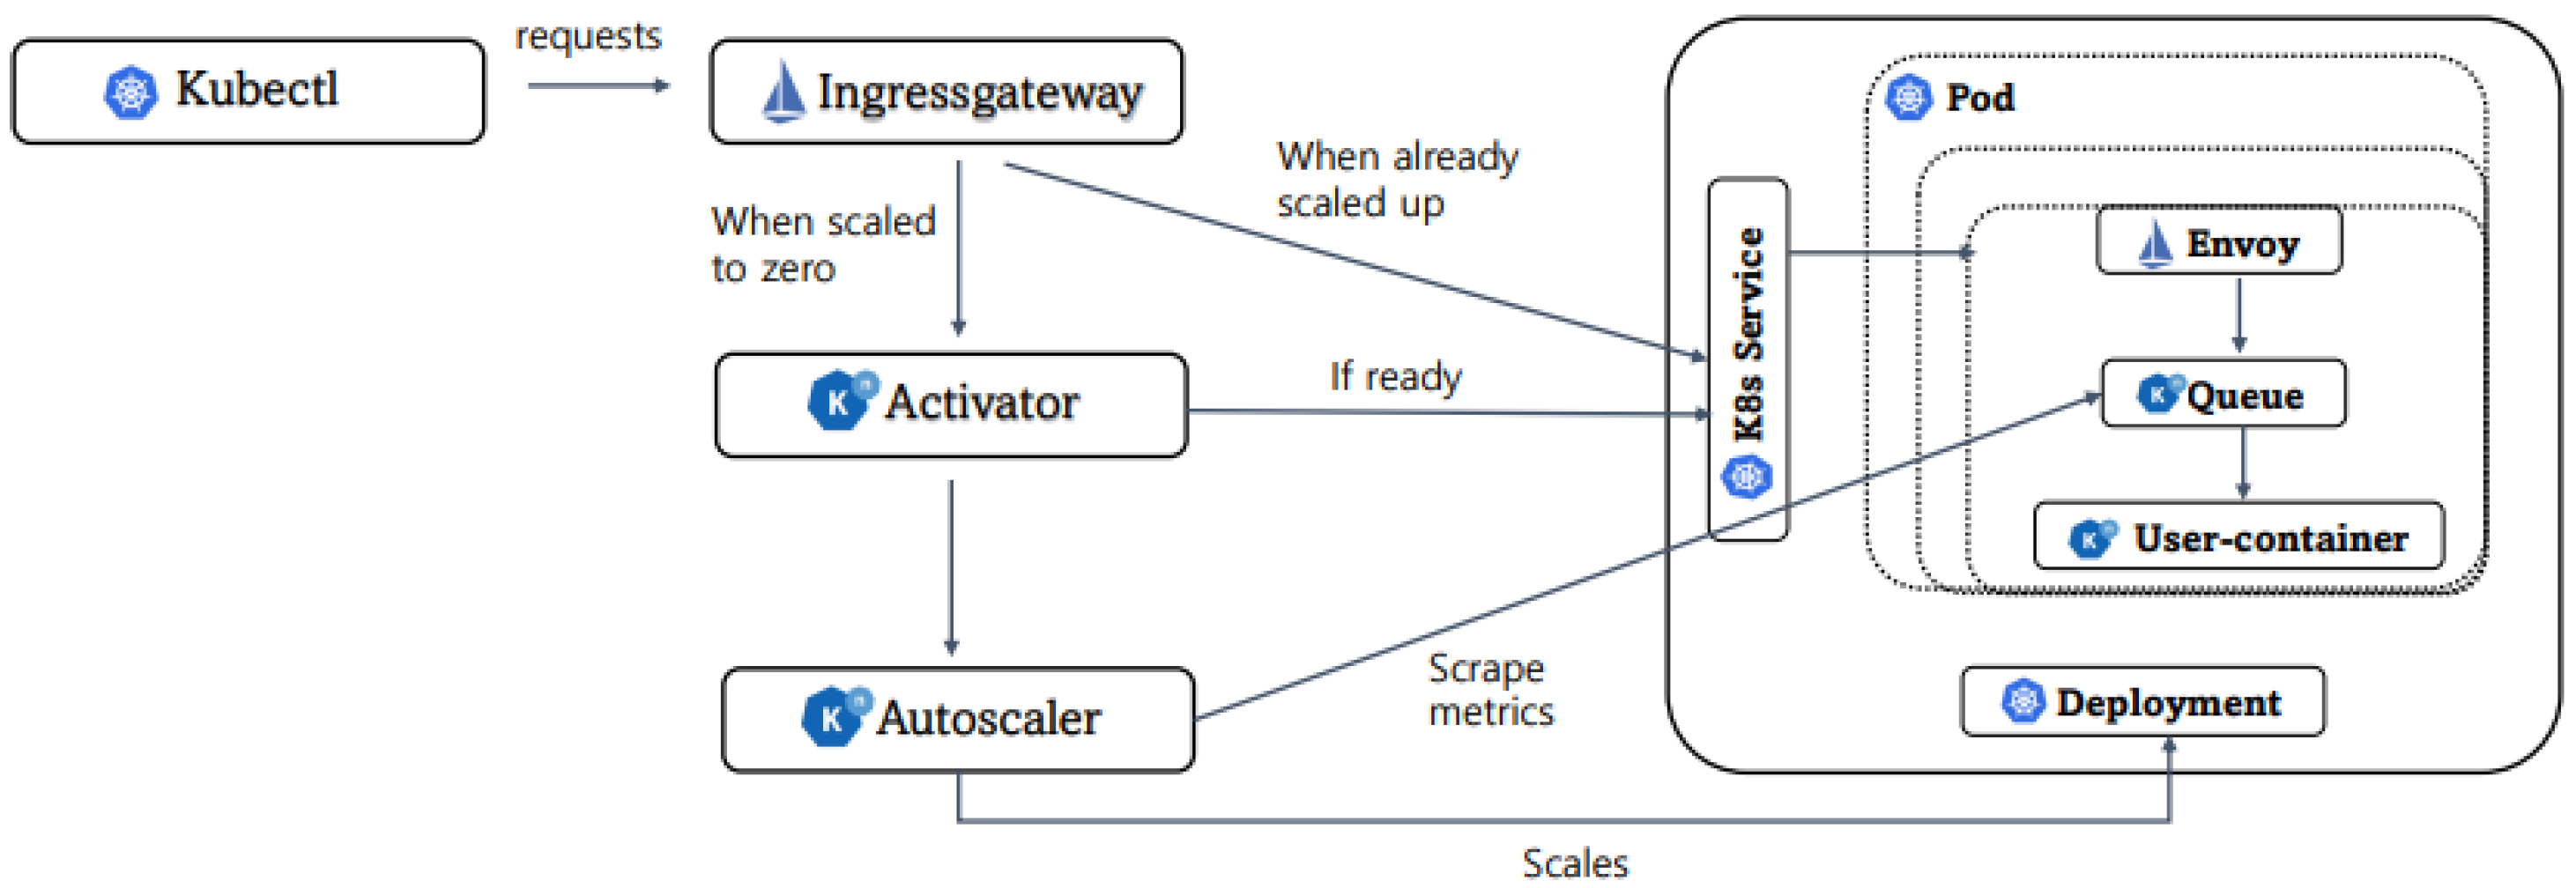
LAN networks can include numerous different devices. A LAN could feature computer systems, smart devices, printers, IoT devices, tvs, and gaming consoles. Routers appoint IP addresses to all gadgets, which identify them on the network. Wide Location Networks are more common in contemporary service. They constitute collections of LANs and cover broad geographical areas.
Software-defined Wide area networks are laid over WAN networks. Agents on connected gadgets connect users to network resources. Managers can manage access by means of safe and secure gateways, and SD-WAN permits extensive traffic tracking.
The network layer is where data is sent. Servers create packages of information, which they send to network gadgets by means of routing gadgets. Packages are then rendered readable at the other end. Mathematical IP addresses generally determine network gadgets. More advanced network architecture uses text labels for the exact same function.
System Defense Fundamentals for Automation Users
Network gadgets are any items of hardware connected to the network architecture. Every network should be documented and mapped.
- interact information throughout the network. - link to router devices and permit personnel secure gain access to. - guards network edges against malicious traffic.
XEvil 5It also checks the status of network devices such as servers or switches and notifies network managers when faults happen. Tracking can be Proactive monitoring is preferable, expecting issues and seeking hazards before they trigger damage.
How Residential IPs Enhance Automation Success
This information could consist of memory use and procedures running on the gadget. Representatives may track user connections or evaluate basic efficiency. Agent-based tracking delivers granular details and boosts network exposure. Nevertheless, the expansion of agents positions problems. Security teams need to set aside time to update and log representatives. Managing large neighborhoods of representatives can be hard for smaller organizations.
It includes packet assessment to find info about information and network use. And it can also include app monitoring to guarantee only confirmed users have access. Agentless monitoring is non-intrusive and requires few resources. It provides an information stream that can be utilized to improve security setups. However this details is generally not granular.
Tracking is not always continuous. Instead, security supervisors to evaluate functionality and security status. The gap in between security examinations is the tracking period. Periods differ depending on gadget type and situation. Service technicians schedule consistent inspections of the internal network. General network efficiency measurements might have longer monitoring intervals. This lowers the load put on the network.
It includes software and hardware developed to identify and obstruct harmful representatives. Protecting networks also encompasses gain access to control, network organization, and security policies. Networking security is. Cybersecurity defend against digital hazards. InfoSec concentrates on data security. Both feed into securing a single computer system linked to the network facilities versus outside threats.
XEvil proxiesThe Future of AI and CAPTCHA Resolution
A well-thought-out security method balances gain access to and protection while likewise satisfying compliance objectives. There are numerous networking security policy ingredients.
Firewall softwares can likewise run internally to create zones of trust, implementing segmentation techniques that limit east-west traffic inside the border. access control tools check all entry requests. Gain access to management entrances ensure just users with the proper qualifications can access network properties. Security policies specify gain access to levels. These policies explain the advantages of each user.
Firewall software defenses likewise avoid illicit access. app security makes sure the appropriate configuration of applications working on the network. The code of apps can be vulnerable to external attacks. For example, attackers make use of vulnerabilities in app code to gain access to network resources. Application security tests all apps and applies patches to upgrade code.












