Proven Bypass Modern Bot Filters
You've managed CAPTCHAs, turned proxies, and spoofed your User-Agent. Your scraper still gets obstructed. Why? Because modern-day anti-bot systems don't depend on a single detection approach. They stack multiple layers and you require to comprehend all of them to develop a scraper that survives in production. This guide maps out every detection technique sites utilize today, from basic to advanced.
Let's go through them all. "Host": "", "Connection": "keep-alive", "sec-ch-ua": '"Chromium"; v="121"', "sec-ch-ua-mobile": "?, 2, 2); const hash = canvas.toDataURL().
Choosing the High-Performance VPS Services in 2026
Most scrapers get blocked at layers 3-4, not 5-7. repairing one layer while neglecting others won't work these catch 55% of bots before JS even runs but they're activated by invisible signals mouse motion and timing matter more each year usage bot detection sites to audit your setup even best stealth can't avoid all difficulties For dealing with the CAPTCHA layer when it sets off, have a look at passxapi-python it supplies a unified API for reCAPTCHA, hCaptcha, Turnstile, and FunCaptcha, so you can focus on the other layers.
In this tutorial, you will find out the following: What Cloudflare is. Top-level methods to bypass Cloudflare. How to bypass the Cloudflare human check in Python.
proxies for XEvilIt offers a comprehensive suite of services developed to make websites much faster and more secure., caching site content on a worldwide network to improve load times and lower latency.
Methods to Scale Network Infrastructure for Automation
By incorporating with Cloudflare's network, sites can rapidly gain improved security and enhanced performance. This can be enabled on any web page served through its global network.
It checks and filters inbound demands in genuine time to stop attacks or unwanted traffic before they reach your servers or access your web pages. As part of its multilayered defense strategy, the Cloudflare WAF uses proprietary algorithms to spot and obstruct destructive bots.
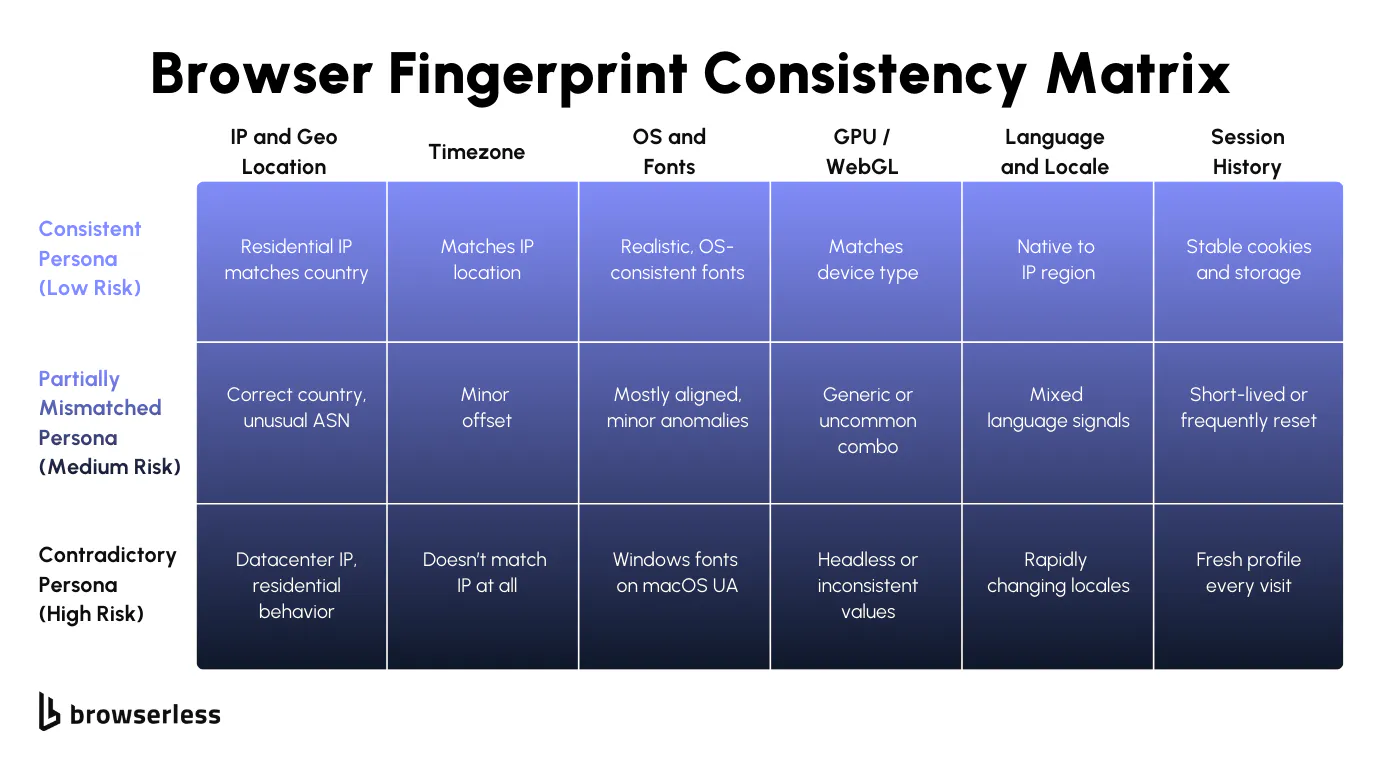
It takes a look at information like the cipher suites provided, the order of negotiation, and other low-level qualities. Bots and non-standard clients frequently have uncommon, non-browser-like TLS signatures that provide them away.: Analyzes HTTP headers, cookies, user-agent strings, and other aspects. Bots often recycle default or suspicious setups that differ from those utilized by real web browsers.
This consists of the specific internet browser version, running system, installed fonts or extensions, and even subtle hardware attributes. These information points form a finger print that helps identify real users from automated scripts.: One of the greatest indications of automated traffic is abnormal behavior. Cloudflare displays patterns like quick demands, lack of mouse movements, identical click courses, idle times, and more.
Cloudflare normally provides 2 modes of human confirmation: Always show the human verification difficulty Automated human verification difficulty (just when suspicious activity is spotted) Check out both options below! The concept is to always require human verification on the very first access to a website.
proxies for XEvilModern Bypass Strategies in Bot Security for 2026
Attempt visiting it in incognito mode (to make sure a fresh session with no cookies), and you will see a CAPTCHA called Cloudflare Gate, even if you are a real human user:: By the time you read this short article, StackOverflow's bot defense might have altered or be working differently. In this case, if you are developing an automated script, the only alternative is to automate the Gate CAPTCHA interaction in a human-like method.
That is how it handles to validate you are human with a single click. In this mode, Cloudflare only issues a difficulty if it suspects a demand may be from a bot. It does this by presenting a JavaScript difficulty, which runs undetectably in the browser to validate that the client behaves like a legitimate user: This procedure is smooth and normally completes immediately if you are a human using a routine internet browser.
Given that this causes very little disruption for routine users, it is by far the most common Cloudflare mode. If the JavaScript obstacle stops working (meaning Cloudflare concludes the client is most likely to be a bot), it will escalate to revealing a Gate CAPTCHA for human confirmation: Now, you are back to what you saw in the previous situation.
Cybersecurity Trends and Expect in 2026
This page is safeguarded by the Cloudflare WAF, so the automated JavaScript-based confirmation process will right away begin. In the background, a series of POST demands are exchanged with Cloudflare's endpoints, sending encrypted information within their payloads: The precise contents of these payloads are not publicly recorded.