Understanding Advanced Rotation for Network Automation

Now, let's take an appearance at what really happens when an automated bot tries to visit a page secured by Cloudflare.: The sample scripts below will be written in Python, but the very same principles use no matter the programs language, HTTP customer, or browser automation tool you select. For this presentation, we will utilize the Cloudflare obstacle page from ScrapingCourse: This is a site that requires passing Cloudflare's verification.
update XEvil V5 installationAs a basic test, we will see what takes place when going to the Cloudflare-protected page above utilizing two various approaches: With an HTTP customer like Requests With an internet browser automation tool like Playwright Check whether Demands can immediately bypass Cloudflare's human confirmation with: # pip set up requests import requests # Connect to the target page action = ("") # Raise exceptions in case of HTTP error status codes response.raise _ for_status() # Confirm if you got the success page html = print("Cloudflare Bypassed:", "You bypassed the Cloudflare obstacle!:D" in html) Note that the script will not even reach the last print() statement.
HTTPError: 403 Customer Error: Forbidden for url: As you can see, Cloudflare recognized the request as originating from an automated script and blocked it with a 403 Forbidden response. Let's now attempt with a internet browser automation solution like Playwright: # pip set up playwright # python -m playwright install from playwright.sync _ api import sync_playwright from playwright.sync _ api import TimeoutError with sync_playwright() as p: browser = (headless=True) page = browser.new _ page() # Go to the target page ("") try: # Wait on the wanted text to be on the page page.locator("text=You bypassed the Cloudflare challenge!:D"). wait_for() challenge_bypassed = Real other than TimeoutError: challenge_bypassed = False # Close the web browser and launch its resources () print("Cloudflare Bypassed:", challenge_bypassed) This script advises a Chromium browser to check out the target page.
High-Speed API Integration for CAPTCHA Solving
Run the needed installation commands and execute the script above. You will see the list below output: Cloudflare Bypassed: False If you run it in headed mode (headless=False), you'll see that the script gets stuck on the Cloudflare verification page. This will reveal a Turnstile CAPTCHA and waits for it to be manually fixed:: If you tried to automate clicking the Turnstile checkbox, the confirmation would fail.
Check out three methods you can use to bypass Cloudflare protection with your automated script. Do not forget that Cloudflare functions as a CDN, which implies it caches and distributes website content across numerous geographically dispersed servers. So, websites dispersed via Cloudflare are generally only accessible through servers in the CDN network.
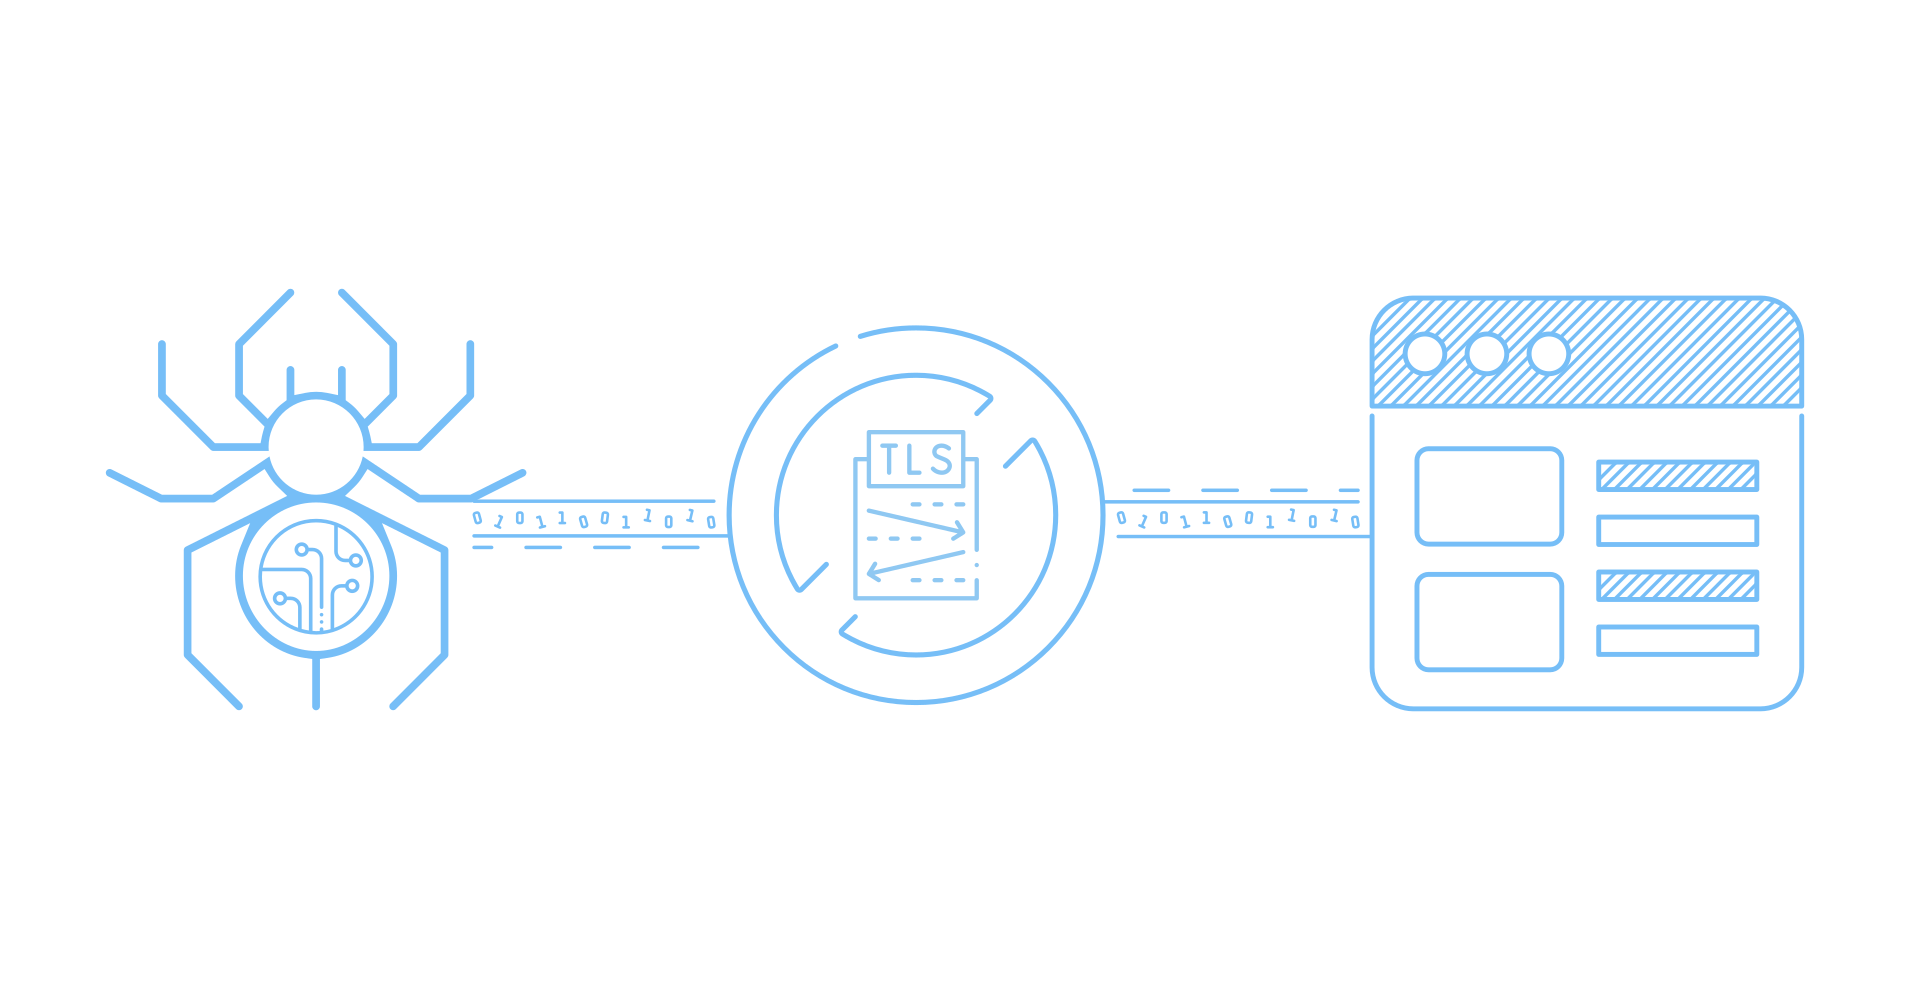
The effect would be that you might interact with the site while bypassing Cloudflare completely. Cloudflare can only assess requests that pass through its network. That is possible by taking a look at DNS history lookup tools like SecurityTrails to identify any historic DNS records that expose the original server's IP address.
The issue is that the server may have additional configurations in place to accept requests only from Cloudflare's IP variety. That would make it nearly difficult to connect to the site straight without being obstructed. Furthermore, successfully finding the original server IP is rather hard and not likely. Online, you can discover numerous free and open-source libraries designed to bypass Cloudflare.
Modern OCR Techniques for Automation Security for 2026
: A lightweight PHP module to bypass Cloudflare's anti-bot pages.: A package to bypass Cloudflare's anti-bot JavaScript challenges. The reason is that designers gave up due to the ongoing struggle to keep up with Cloudflare's updates.
To be efficient, these libraries or online services need to offer a minimum of the following features: JavaScript rendering, so that Cloudflare's JavaScript obstacles can be executed correctly. TLS, HTTP header, and web browser fingerprint spoofing to replicate real users and prevent detection. Gate CAPTCHA resolving abilities, to deal with Cloudflare's human verification when it appears.
Furthermore, premium solutions typically include an integrated proxy network to rotate IP addresses and minimize the risk of getting blocked. In the following two chapters, you will see both open-source and mainly exceptional solutions in action! Many open-source options that claim to bypass Cloudflare only handle to do so for a limited time period.
So, it is not a surprise that lots of tools that once worked (like Puppeteer Stealth) no longer achieve the goal. Still, at the time of composing, there are two options that in fact manage to bypass Cloudflare's securities:: An open-source, anti-detect Python web browser based on a customized Firefox construct, developed to avert bot detection and make it possible for web scraping.